Close the 3 gaps in your XDR/EDR and respond safely in a timely manner
Swiss SOCaaS with 24/7 threat detection for SMEs
Comprehensive protection for your IT, cloud, OT and IoT
The 3 gaps in your XDR/EDR approach

Not all systems included in XDR/EDR monitoring
The signals from your VPN, firewall and Active Directory will be e.g. B. not observed by your XDR system
No reliable and timely processing of signals and alerts
Your internal/external IT has many other tasks. Too often, relevant security signals and alerts remain dormant for days or even weeks
Complex risk signals are difficult to detect and alert
Due to separate observation in XDR and other systems, it is difficult to connect multiple signals to form an incident. This is impossible for unobserved systems
How we close these gaps

Central collection and consistent analysis and processing of all relevant log data from all systems in a SIEM and SOAR Tool (Microsoft Sentinel)
Initial analysis and triage of all incoming alerts within 30 minutes (depending on service level)
Specialized tools and many years of security specialists experience enable the detection of critical signal combinations by correlating individual signals
Constant optimization of automated detection of potentially dangerous signals
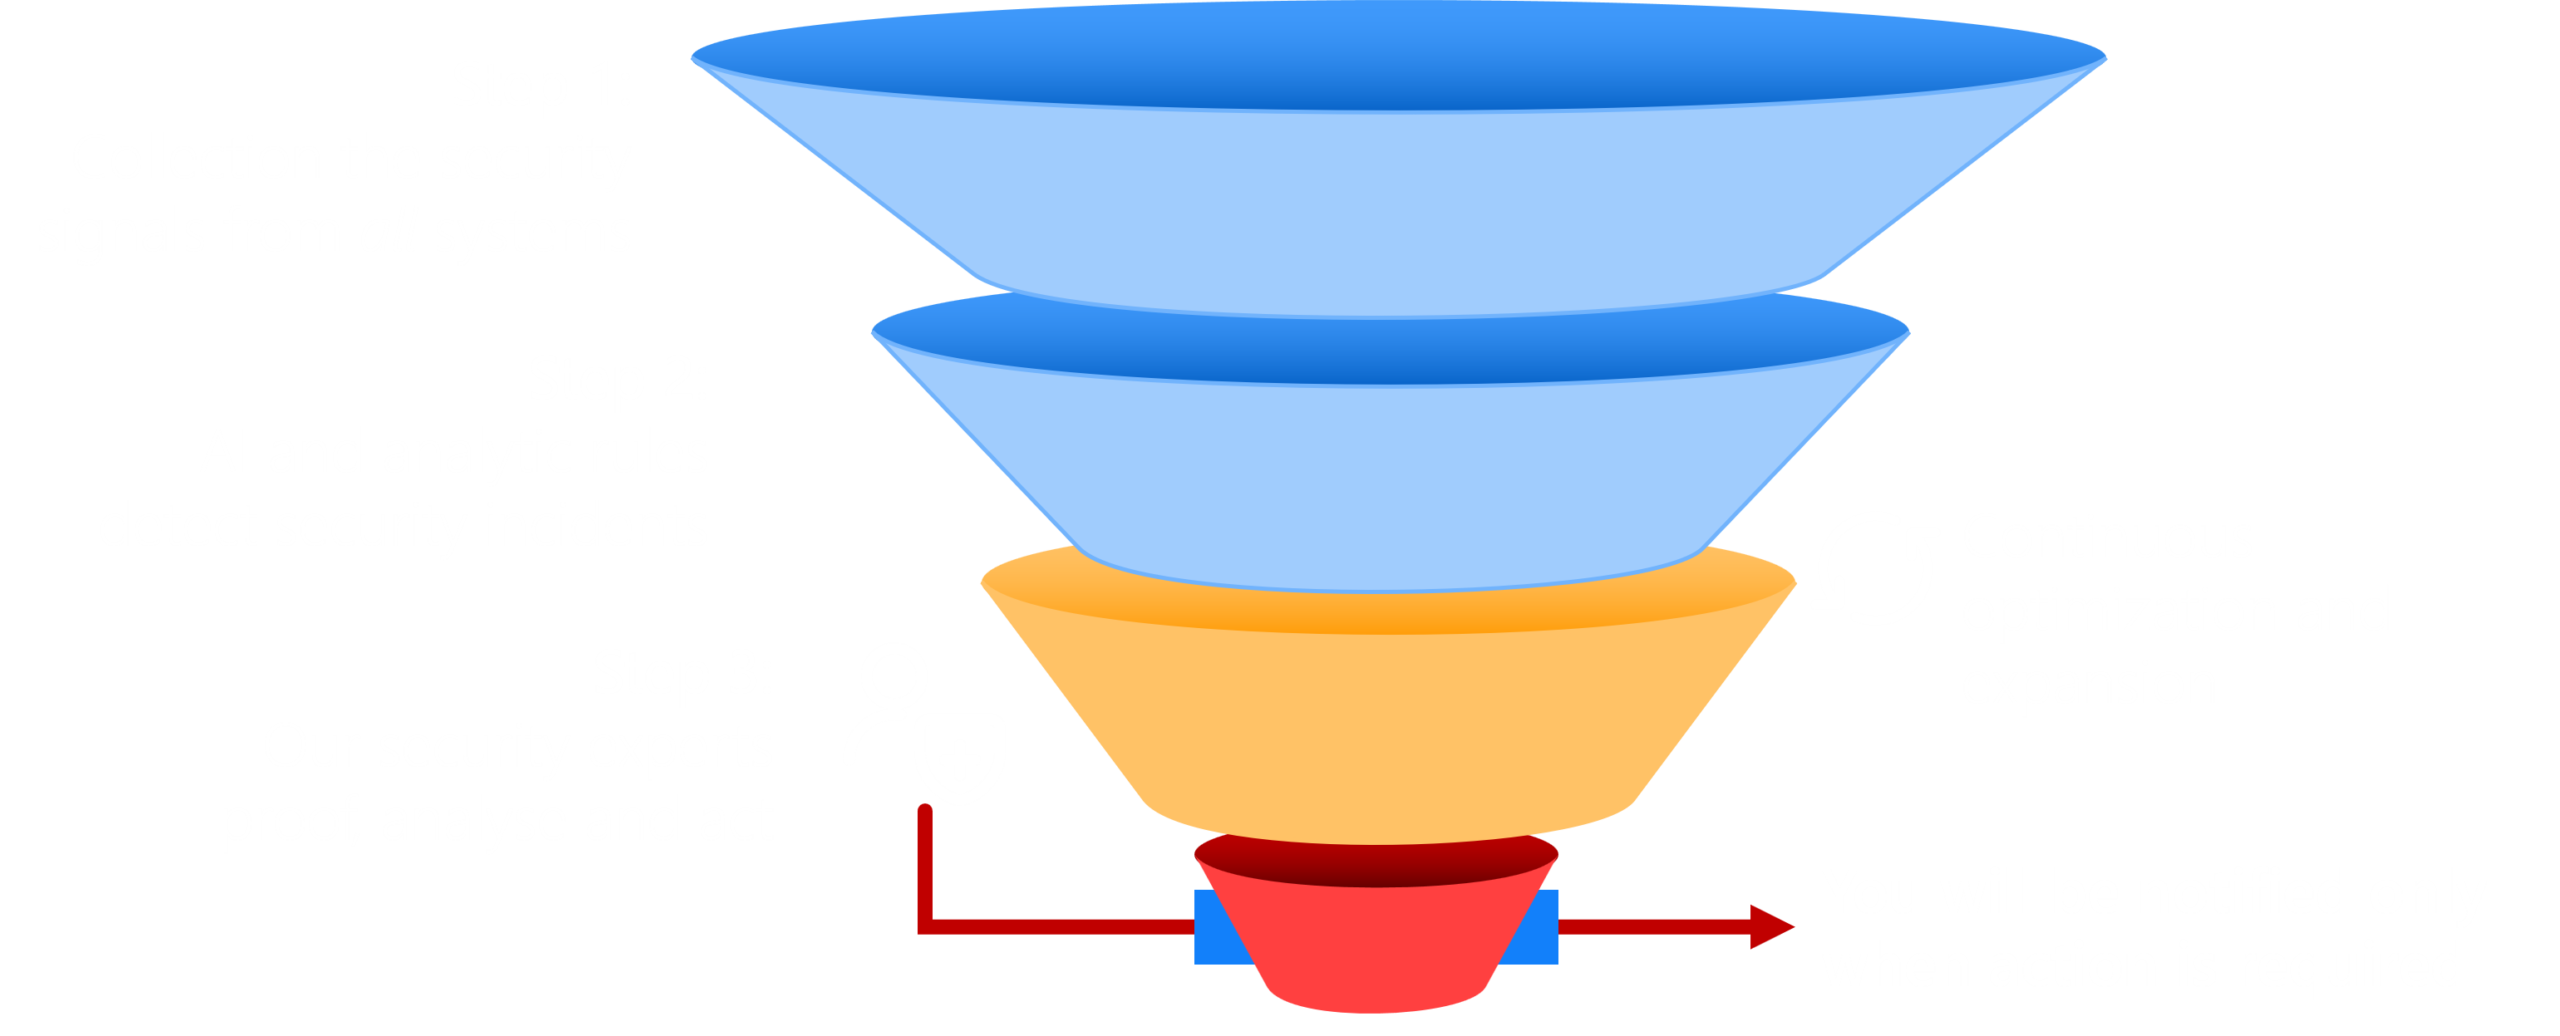
We will only get in touch if you need to act yourself
- Monitoring of all Systems
- Automated preselection, based on many years of experience, rules and AI
- Evaluation & handling by our security specialists
- Only the relevant alerts get escalated to you
What our customers say about us
A monthly fixed price for many services
- Made in Switzerland – built on Microsoft
- SIEM & SOAR – Security Monitoring & Alerting
- Microsoft Security AI-assisted detection & analysis
- MXDR-integrated with your existing solution
- User & Entity Behavior Analytics detect anomalies
- Threat Intelligence – Global and local coverage
- Rapid & qualified alerting in case of incidents
Budget security and probationary period

Fixed monthly flat rate
From monthly CHF 950 you are there. If you wish, you can expand the service as you wish
Fair prices
They only pay for the incidents that our security analysts have to look at
3 months trial period
During 3 months you can cancel the SOC Service within a week - no long-term contract commitment
To peace of mind in just one week

Most of our customers are completely onboarded within one to two weeks, and even faster if desired (e. g. as part of an incident to provide very timely support)

Our process is well-rehearsed, efficient and requires little cooperation from you

How to get from the thought „We need support“ to the comforting feeling „We are well protected“ in no time

Your data never leaves your Microsoft Tenant. Deployment and management take place in your environment – for full transparency and control
Certifications

Information Security Management System (ISMS) according to ISO 27001:2022
The certificate confirms that the requirements from the ISO standards are systematically implemented in FusionOne AG. Our ISMS includes all business areas and all SOC services provided to our customers.
FAQ
What if we already have an IT provider?
That’s not a problem – we’re not here to replace him. We work with your existing IT team or provider and do exactly what they usually can’t do: 24/7 threat monitoring and response. See us as an additional layer of security, not as competition.
Can I really trust a service that is not in-house?
Yes—that actually makes it even safer. Our team works independently, which means no conflicts of interest and full transparency. You get trained experts reviewing your systems, completely free of internal politics.
What makes this better than our existing security tools?
Tools don’t stop threats—people do. Most security tools only send alerts; someone still has to take action. Our SOCaaS combines these tools with a team of experts who monitor, respond, and resolve issues in real time.
Does this work with our Microsoft 365 environment?
Absolutely. We specialize in protecting Microsoft 365 and on-premises Active Directory environments. You’ll receive end-to-end coverage without any changes to your team’s usual workflow.
How quickly can we start?
Most customers are fully onboarded within one to two weeks. Our process is so well-established that you’ll quickly go from thinking, “We need help,” to “We’re protected.”
Is the service worth it for an SME?
Yes. You get enterprise-level security without having to build your own in-house team. This is significantly less expensive than the costs that a single serious security incident would incur.
Do you only monitor our cloud or also our on-premises network and devices?
We specialize in protecting Microsoft 365 and Active Directory environments – both on-premises and in the cloud. We cover all networks, systems, and devices, ensuring that your entire IT environment is fully secured.